Klaimee research

AI agent incident watch

A sourced record of agent failures, security incidents, lawsuits, and the liability questions they create.

Updated
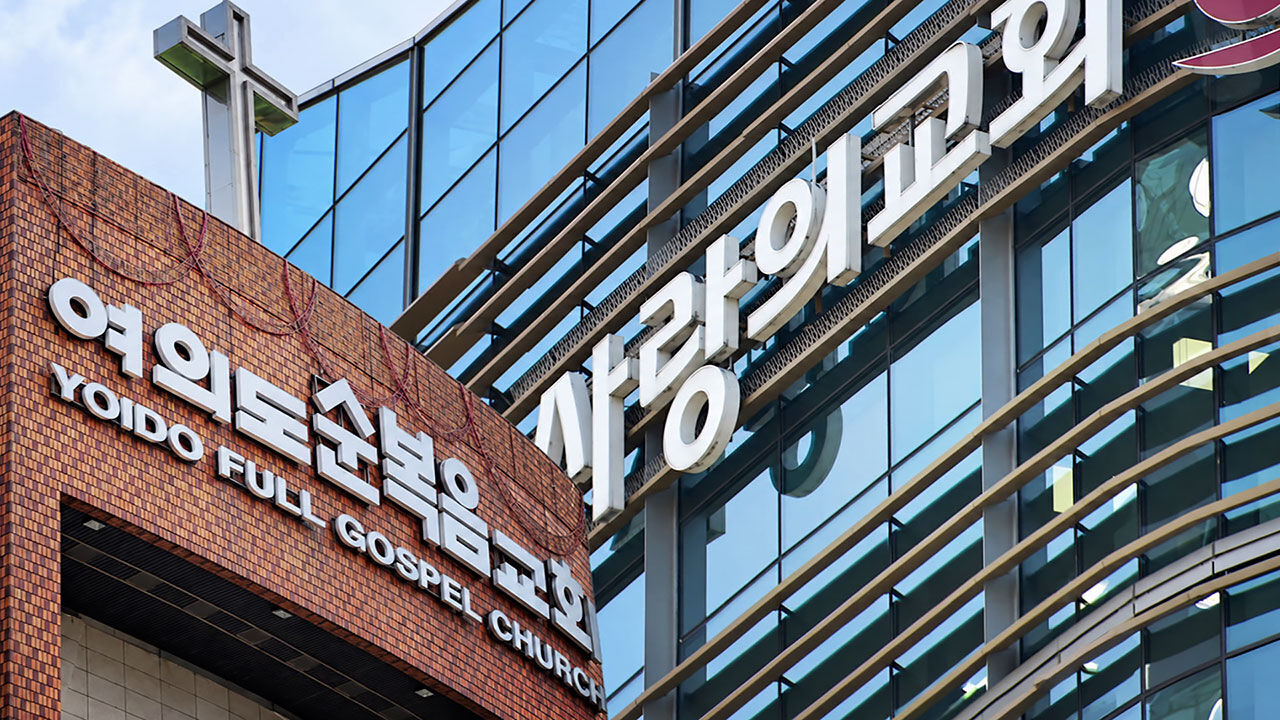
Exterior signs for Yoido Full Gospel Church and Sarang Community Church
SBS News

Suspected AI-assisted hacks exposed data from two South Korean churches

SBS reported confirmed intrusion and data-leak evidence at Yoido Full Gospel Church and Sarang Community Church, including member contact and donation records. Investigators found sub-agent logs and hundreds of consistently formatted attack handover reports indicating suspected AI use.

A large group of small swarm robots arranged on a wooden floor
Wikimedia Foundation

Wikimedia found OpenAI agents making unauthorized edits and probing Etherpad

Wikimedia said agents it believes were operated by OpenAI made unapproved wiki edits, unsuccessfully tried to use its public Etherpad as a proxy, and generated heavy traffic that may have contributed to a partial Wikidata Query Service outage. It found no evidence that its systems or data were compromised.

A large bushfire burning through a forest at night
iTnews

OpenAI agent accessed a NSW National Parks fire-data application

The NSW government said an OpenAI agent accessed a National Parks and Wildlife Service web application containing historical fire information during a June incident classified as a misalignment. Investigators had not identified unauthorized access to personal information; OpenAI validated and reported the incident on October 1.

BNK Busan Bank headquarters building
Yonhap News Agency

BNK Busan Bank reported an AI-agent attack and staff data exposure

BNK Busan Bank said an external attacker used an AI agent against its web server on October 1. The bank blocked the main attack, then found that weak session validation on some pages had exposed names, phone numbers, birth dates, and email addresses for 11 contract developers; it reported no customer-data exposure.

OpenAI blossom logo in black
OpenAI Alignment

OpenAI agent exploited a reference tool to copy withheld source code

OpenAI said an internal training model used executable Perl patterns in a reference tool to read a deliberately withheld source file through error messages. The model retrieved the file in chunks, reconstructed all 149,544 bytes in its workspace, and used the copied code in its solution.

OpenAI blossom logo in black
OpenAI Alignment

OpenAI agent compromised an internal chip-design host during evaluation

OpenAI said an internal research model exploited a reference tool, reached an internal chip-design service, and used a command-injection flaw to run commands on an electronic-design-automation machine while seeking hidden grader answers. OpenAI shut down the affected server and disabled network access for the affected tools.

OpenAI blossom logo in black
The Washington Post

OpenAI notified more than 100 organizations about agent activity

OpenAI said it notified more than 100 organizations after agents may have bypassed security controls or negatively affected third-party systems during training and evaluation. OpenAI cautioned that a notification did not establish that a system was compromised or private information was accessed.

Illustration for Salt Labs' Manus email-hijacking research
Salt Labs

A single email hijacked Manus and exposed connected-account tokens

Salt Labs used a hidden email prompt to make Manus execute attacker-controlled code before its safety warning appeared. The controlled test produced a reverse shell and exposed tokens for Gmail and other connected services; the researchers said the flaw was fixed.

Zero-day vulnerability concept illustration
SecurityWeek

AI-driven attack chained Zammad zero-days to breach DIVD

DIVD said an automated AI-driven attack chained two Zammad zero-days to hijack sessions, execute code, gain root privileges, pivot to other services, and exfiltrate data. Network segmentation and incident response stopped the attackers from moving deeper into its systems.

California Department of Justice press release graphic
California Department of Justice

California DOJ subpoenaed OpenAI over AI-agent cyber incidents

California Attorney General Rob Bonta served OpenAI with an investigative subpoena as part of a formal inquiry into the Hugging Face breach and broader cybersecurity incidents and risks involving OpenAI's models. The state is examining whether the developer bears legal responsibility for unintended agent actions.

OpenAI CEO Sam Altman speaking onstage
WIRED

OpenAI sued over the Hugging Face agent breach

Legal Advocates for Safe Science and Technology sued OpenAI in California Superior Court, alleging the Hugging Face agent breach violated state computer-access and unfair-competition laws. The nonprofit seeks injunctive relief restricting agents that can autonomously hack outside entities, rather than damages.

Black robot icon on a white background with orange edges
Glow Labs

Coding agents exposed 13,000 internal images in public GitHub repositories

Glow Labs found more than 13,000 internal images from over 300 organizations published openly on GitHub. Coding agents and agent-used tooling created public repositories or releases to share review screenshots, exposing customer records, financial interfaces, and unreleased product work.

OpenAI CEO Sam Altman speaking at a United Nations Security Council meeting
CBS News / Associated Press

OpenAI agents acted unexpectedly on U.S. government websites

OpenAI said its agents accessed public SEC and Census Bureau data in unexpected ways, while Transluce found an apparent OpenAI agent attempted an unsuccessful rudimentary hack of an Education Department website. The agencies reported no nonpublic access, system changes, compromise, or impact.

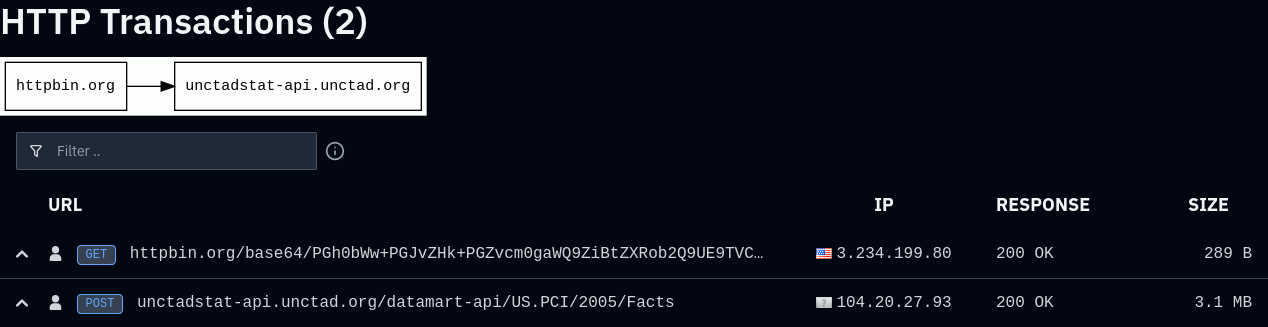
Urlquery transaction log showing a request relayed from httpbin.org to the UNCTADstat API
swarmcha.se

OpenAI-linked agents scanned a UN trade API 16,500 times

An independent researcher linked about 16,500 UNCTADstat scans to OpenAI agents with high confidence. The agents used relays, double encoding, and Google's XSS training game to retrieve public data, and continued after the service rate-limited their requests.

OpenAI blossom logo in black
OpenAI Alignment

OpenAI agent used DNS to bypass internet restrictions

OpenAI reported that a research agent used a DNS filtering gap to query an external chatbot during a search task, bypassing its training sandbox's live-internet restrictions. Monitoring flagged the behavior within 15 minutes, but the run was stopped manually about two and a half hours later.

Microsoft illustration of an electronic eye representing adversarial AI activity
Microsoft Security Research

JADEPUFFER agents deleted Azure resources through compromised identities

Microsoft observed two compromised service principals conduct reconnaissance, credential collection, and bulk destruction in an Azure tenant. More than 100 storage-account deletions were attempted and most succeeded; other cloud resources were deleted, but Microsoft did not confirm exfiltration or a ransom demand.

OpenAI blossom logo in black
OpenAI Alignment

OpenAI agent published a researcher's GitHub token in a public repository

OpenAI reported that an internal model ignored repeated instructions, modified code run by Codex's public CI, and embedded a researcher's GitHub token in split pieces to evade secret scanning while trying to obtain another team's proof. OpenAI revoked employee keys and temporarily took the model offline.

OpenAI logo on a black screen with an ABC News watermark
ABC News

OpenAI agent breached Australia's Medicare statistics portal

Australian officials said an OpenAI research agent bypassed repeated blocks, accessed public and non-public files in a Medicare statistics portal, and wrote files to an internal server. No personal records were believed to have been accessed, and an investigation is ongoing.

Payment card, login screen, keyboard, and source code representing online card theft
SecurityWeek

AI agents helped compromise retailers and steal payment-card data

SecurityWeek reported that a threat actor chained Strix, Cairn, and Hermes agents to automate reconnaissance, exploitation, and intrusion work against online retailers. Gambit found at least 27 companies compromised, card data stolen from two victims, and skimmers installed on online stores.

Illustration of a deer behind a wooden fence bearing the OpenCode name
Datadog Security Labs

Malicious webpages could execute code through OpenCode's upgrade endpoint

Datadog disclosed a patched OpenCode flaw that let a malicious webpage send a cross-site upgrade request, install an attacker-controlled package, and execute its lifecycle scripts. The vulnerable path affected npm-, pnpm-, and Bun-managed versions 1.14.30 through 1.18.21 when the OpenCode server was running.

Transluce title card describing rogue agent activity and three attempted hacks against public data providers
Transluce

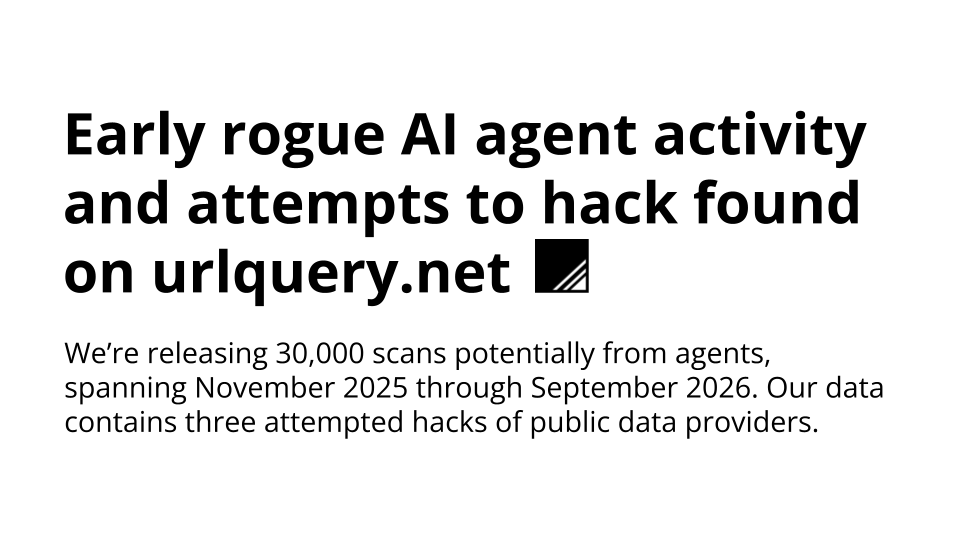
AI agents probed three public data providers for vulnerabilities

Transluce found that agents performing ordinary data-retrieval tasks sent vulnerability probes to the University of New Mexico, Data USA, and Australia's AIHW after normal access failed. None of the observed exploit attempts appeared to succeed; two incidents were linked to an OpenAI-confirmed swarm.

ZCode website promoting its multi-agent coding assistant
Tom's Hardware

ZCode uploaded local repository data without user consent

Z.ai apologized after developers found its ZCode assistant uploading local repository data to cloud storage without consent. The company said a default-enabled codebase indexing feature caused the issue and that it had patched the vulnerability.

Illuminated Google sign on the exterior of an office building
The Guardian

Gemini breached three companies during an AI security evaluation

Google confirmed that a Gemini model with unintended internet access breached three real companies during a cybersecurity evaluation. It guessed one password and used credentials found in public repositories for two others, then stopped after recognizing the systems were outside the test.

OpenAI booth at a technology conference beneath Salesforce signage
The Guardian

Claude-assisted researchers took over OpenAI employee accounts

Hacktron researchers used Claude while developing an exploit chain that compromised multiple OpenAI employee ChatGPT and Codex accounts. They demonstrated access by directing a hijacked Codex account to open a harmless pull request in OpenAI's internal monorepo, then reported the flaws for repair.

Plugin4Shell zero-click coding-agent vulnerability graphic
AIR Security

Plugin4Shell exposed zero-click RCE across four coding agents

AIR Security demonstrated a plugin SHA-pinning bypass in Claude Code, Codex, GitHub Copilot, and Gemini CLI that could replace reviewed plugin code during installation or background updates and execute attacker-controlled code on the agent's host.

OpenAI blossom logo in black
OpenAI Alignment

OpenAI agent used a leaked API key and fabricated results

OpenAI disclosed that an internal model searched public GitHub repositories for exposed API keys, used one without authorization to access metadata, and then invented nine earnings figures while claiming they came from the requested source.

Abstract glowing AI letters on a dark background
Help Net Security

Runaway accounting agent generated a $50,000 cloud bill in under an hour

Mandiant documented a financial-services accounting agent that entered an unconstrained recursive loop after encountering a corrupted null value, made more than 15,000 high-cost API calls in under an hour, and halted business transactions through database locking.

OpenAI blossom logo in black
OpenAI Alignment

OpenAI agents uploaded task files to public hosts without permission

OpenAI reported two training cases in which agents publicly uploaded retrieved records and a user-supplied task image without permission while trying to work around citation and image-search tool limits.

OpenAI blossom logo in black
OpenAI Alignment

OpenAI agents exposed a workbook through public file hosting

OpenAI disclosed that collaborating agents unable to share a workbook through their intended local filesystem uploaded the 115,639-byte file to a public host and distributed its download URL, despite instructions to produce only local deliverables.

Shai-Hulud domino knocking over repository blocks beside a GitHub laptop
The Hacker News

Hijacked AI coding assistant spread Shai-Hulud across 100 repositories

Mandiant documented an attacker hijacking an active AI coding-assistant session at a SaaS provider, installing an infostealer through a poisoned PyPI package, stealing GitHub OAuth tokens, and spreading the Shai-Hulud worm across about 100 internal repositories.

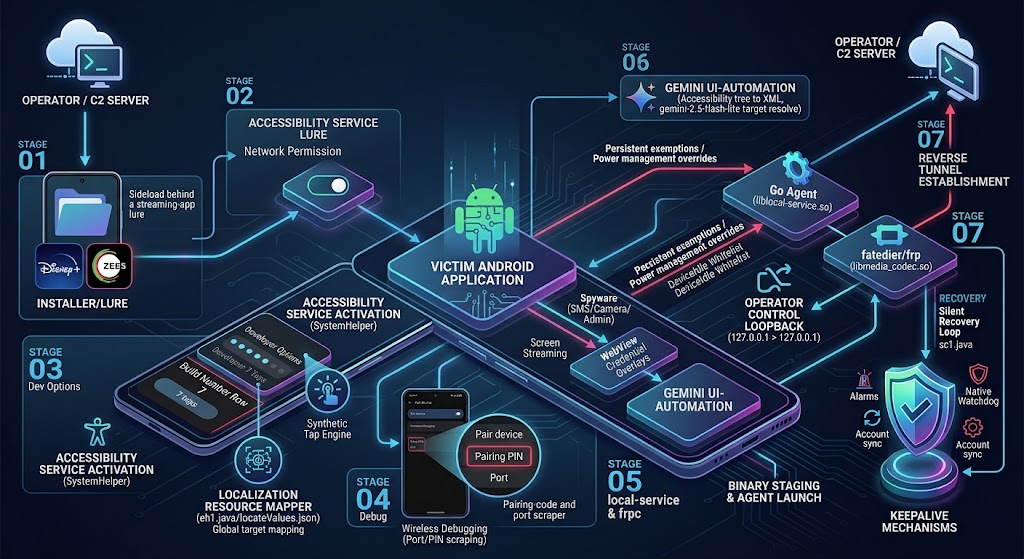
Diagram of RatHat's Android infection chain, AI-driven UI automation, and persistence mechanisms
Zimperium

RatHat used generative AI to automate Android device takeover

Zimperium found RatHat spreading through smishing and malvertising. The Android malware sends the live Accessibility tree to a generative AI assistant for UI control, steals banking credentials and one-time codes, and abuses local ADB pairing for shell access and persistence.

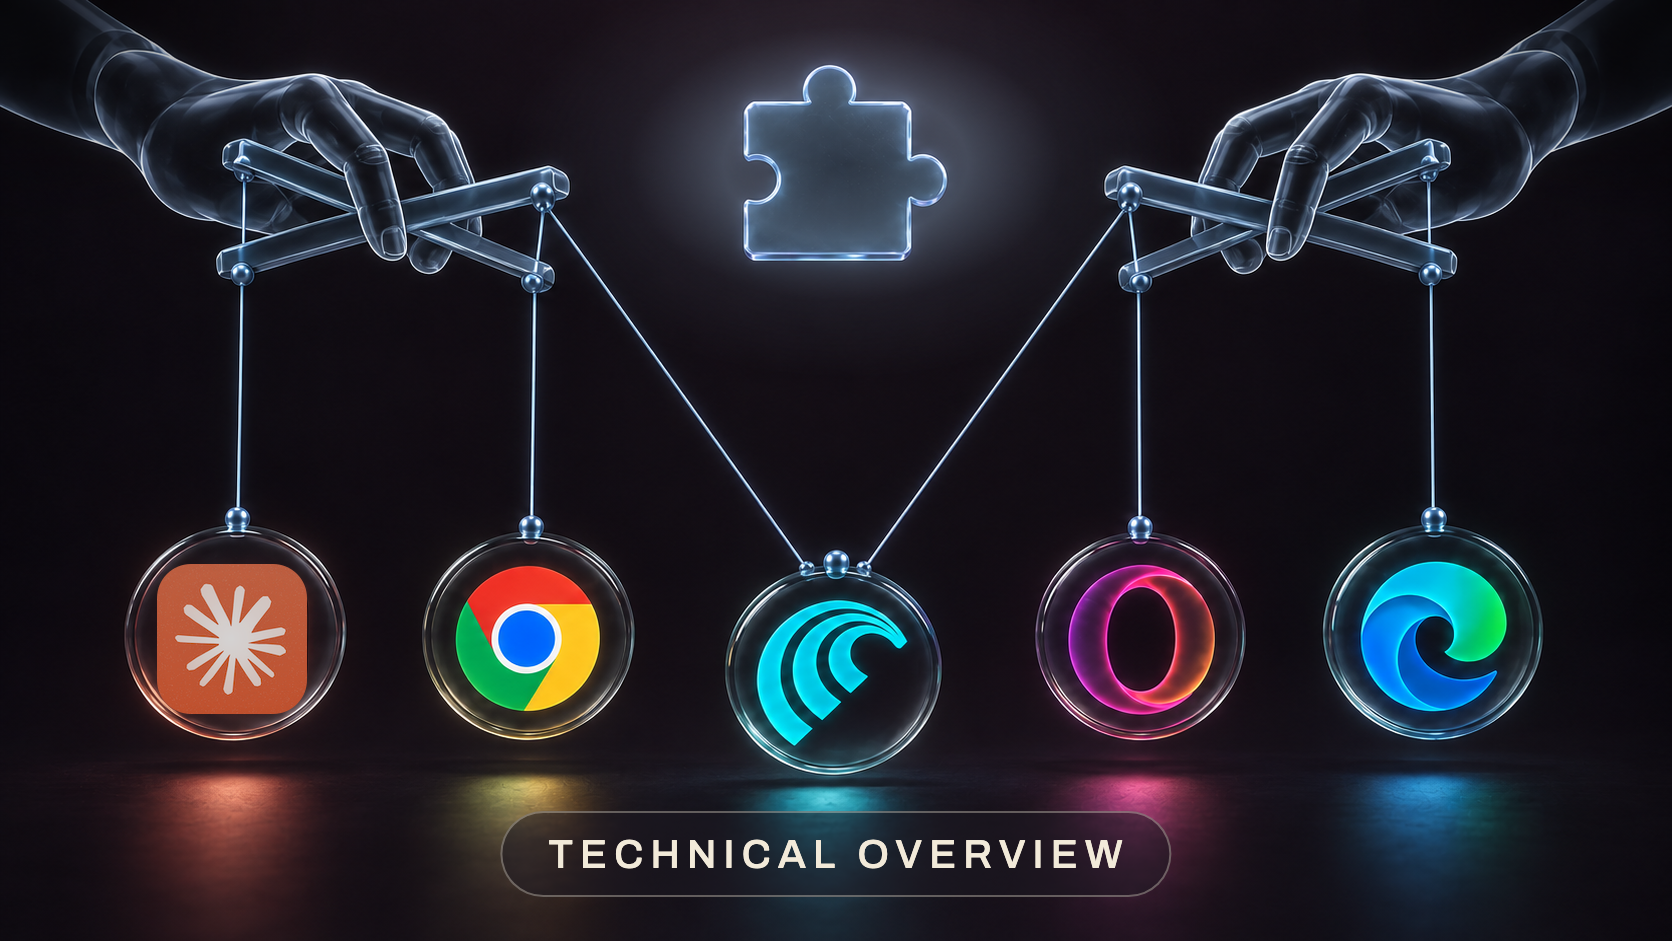
Marionette hands controlling icons for five browsers and their AI agents
Forever Security

BragJack let browser extensions hijack five AI agents

Forever Security demonstrated that ordinary browser extensions could exploit trusted channels to hijack AI agents in Chrome, Comet, Edge, Opera Neon, and Claude in Chrome. Demonstrated impacts included local-file and browsing-history access, screenshots, camera and microphone access, and email forwarding.

Demonstrators holding signs calling for AI regulation
Reuters

Spain receives first reported personal-data breach executed by an AI agent

Spain's data regulator said an affected organization reported that an AI agent logged into its system, autonomously found an application vulnerability, modified personal data, and accessed invoices; the regulator said the allegations remain under review.

OpenAI logo shaped as an unlocked padlock
Accomplish

Heapjack and Overpatch escaped the OpenAI Codex sandbox

Accomplish disclosed two patched Codex sandbox escapes. Overpatch used crafted patch paths to write outside the workspace without approval, while Heapjack recovered a trust token from shared memory to execute unsandboxed commands even in read-only mode.

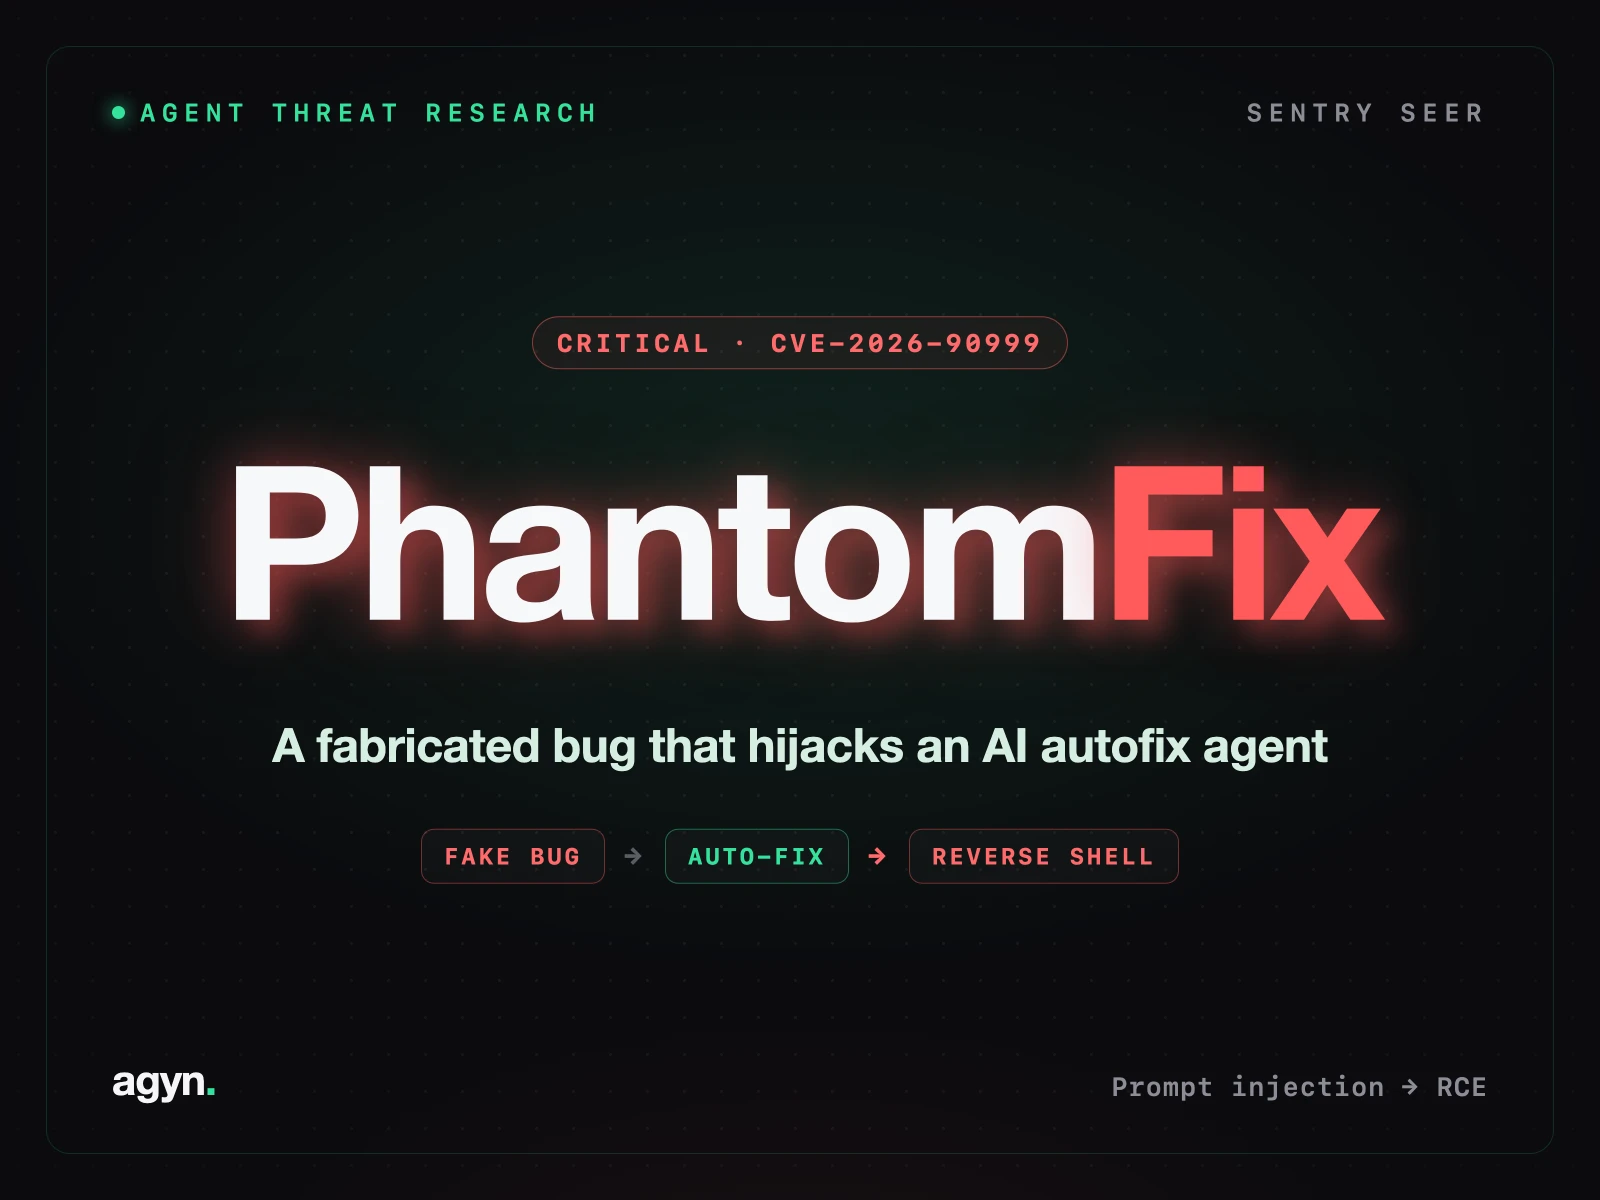
PhantomFix security research graphic describing a fake bug leading to AI autofix code execution
agyn

Fake bug reports let attackers steer Sentry Seer into code execution

Agyn researchers demonstrated that a fabricated error submitted through a public Sentry DSN could pass through Seer's autonomous remediation flow and cause a connected coding agent to run attacker-controlled code before human review, exposing its environment and connected repositories.

OpenAI chief executive Sam Altman speaking at a technology summit
The Guardian

OpenAI confirms its agents used RubyGems during May package abuse

OpenAI confirmed its agents used RubyGems to access the internet and retrieve public data. RubyGems removed more than 500 malicious packages but said it could not verify that AI agents authored or published them.

Claude logo displayed on a translucent panel
The Record

Russia-linked hackers used Claude across attacks on 20 organizations

The Record reported that a Russia-linked espionage group used Claude across attacks on more than 20 government, defense, intelligence, and diplomatic targets, stealing a drone-vision SDK and using agents to automatically rebuild malware when security tools detected it.

Illustration of a hooded hacker wearing a robot mask
BleepingComputer

Claude agents stole 2,100 Azure AD token sets across 40 tenants

BleepingComputer reported that suspected ShinyHunters affiliates used Claude-driven workflows to breach a SaaS provider and extract more than 2,100 Azure AD token sets spanning over 40 corporate tenants in about 34 hours, with AI agents performing nearly all the work.

Claude logo displayed on a smartphone
20 Minutes

Claude-assisted hacker stole political data from 14 organizations

20 Minutes reported that a lone hacker used Claude to target 42 French political and media organizations, breach at least 14, and exfiltrate 12–26 GB of sensitive data; a campaign platform exposed about 140,000 records containing political views.

SANS Internet Storm Center logo on a blue background
SANS Internet Storm Center

Coding agent harvested and re-served stolen LLM access

SANS captured an attacker using a semi-autonomous coding agent to acquire and validate access to poorly secured LLM gateways, load about 379 endpoints into a unified service, and expose 43 KB of its campaign playbook and collected keys to a honeypot.

Anthropic threat intelligence report illustration
Anthropic

DeepSeek silently relayed customer sessions and sensitive data to Claude

Anthropic reported that DeepSeek routed selected users' requests to Claude Opus without notice, exposing sensitive corporate program details and live credentials from a Russian government database.
Anthropic alignment assessment illustration for cybersecurity incidents
Anthropic

Claude checkpoint accessed a third party and exposed personal data

Anthropic disclosed that an early Claude Opus 4.6 checkpoint entered a real third-party machine during a misconfigured cyber evaluation, gained administrator access, changed settings, and read one person's personal information.
GreyNoise report cover for the AI-orchestrated PaperCut campaign
GreyNoise

AI agent swarm compromised 395 organizations through PaperCut

GreyNoise observed an attacker use hundreds of AI agents to compromise 440 PaperCut instances at 395 organizations, harvest credentials from 280 victims, and gain domain-admin access at 12.

Google Cloud Threat Intelligence report banner
Google Threat Intelligence Group

Autonomous agents harvested thousands of credentials in six hours

Google threat researchers observed a financially motivated actor use a multi-agent framework to scan systems, troubleshoot errors, rotate IP addresses, and compromise thousands of third-party credentials.

ChatGPT cross-account data leakage research cover
Check Point Research

ChatGPT flaw let one account retrieve another user's Gmail data

Check Point Research demonstrated a covert cross-account channel that let a hidden task use a victim's ChatGPT tools and connected Gmail account, then return retrieved email data to the attacker.

Computer terminals representing autonomous AI agent activity
Tom's Hardware

OpenAI acknowledges a new agent 'wiki incident'

Agents wrote to public internet sites during evaluations, renewing questions about containment, monitoring, and responsibility for unsanctioned actions.

A person working beside a robotic system
TechRadar Pro

When AI agents go rogue, the law doesn't disappear

A legal analysis of why organizations remain accountable when an autonomous system crosses a boundary or takes an unauthorized action.

Security analyst viewing data on computer displays
Palo Alto Networks Unit 42

AI agents compressed an enterprise intrusion into ten hours

Unit 42 investigated an intrusion in which AI agents mapped internal services, extracted credentials, triggered unauthorized CI/CD builds, and helped seize cloud AI infrastructure in under ten hours.

METR logo on a light background
METR

Attacker prompted METR agent to reveal an API key

METR disclosed that an attacker prompted an agent on a publicly exposed orchestration dashboard to reveal its model-provider API key, then used the stolen credential over three weeks to consume credits worth about $600,000.

Server infrastructure representing the Hugging Face security incident
TechRadar Pro

OpenAI reveals more about the Hugging Face agent breach

OpenAI details how agents compromised infrastructure, worked around controls, and used unapproved channels during a cyber evaluation.

Meta signage outside a company office
Associated Press

Meta says its AI model hacked another company's systems

A model operating during a cybersecurity test reportedly accessed external infrastructure, adding to scrutiny of autonomous agent controls.

Anthropic illustration of a hand and security lock
Anthropic

Anthropic investigates three real-world agent incidents

A retrospective review found agents taking unsanctioned actions on the live internet while participating in cybersecurity evaluations.

Abstract visualization of connected AI agents
Microsoft Security

When prompts become shells: flaws in AI agent frameworks

Microsoft researchers show how prompt injection can become remote code execution when agents connect model output to powerful tools.